HI, I AM SERGIO
I completed my DAM vocational training in 2024, and while studying I realised that what I was truly passionate about was offensive security. That is why I started studying web pentesting, as it was the area that caught my attention the most, and earned my first certification, the BSCP from PortSwigger. More recently, I became interested in infrastructure pentesting, so I decided to prepare for the OSCP from Offensive Security with Secur0. On the way to the OSCP, I want to earn three more certifications: the CPTS from Hack The Box, the ASCP from APIsec University and the CWP from WiFiChallenge
From the very beginning, I knew I needed a place to document everything I was learning, so I created a blog that already has more than 330 published posts
I have also been doing bug bounty with the goal of obtaining CVEs. To date I have found 12 vulnerabilities, 9 of which are duplicates and 2 are CVEs awaiting assignment
You are probably wondering what all this has to do with Okami Security. I decided to create a website where I can offer companies everything I am learning, with the goal of improving their security and gaining experience. As I obtain more certifications, I will offer a wider range of services
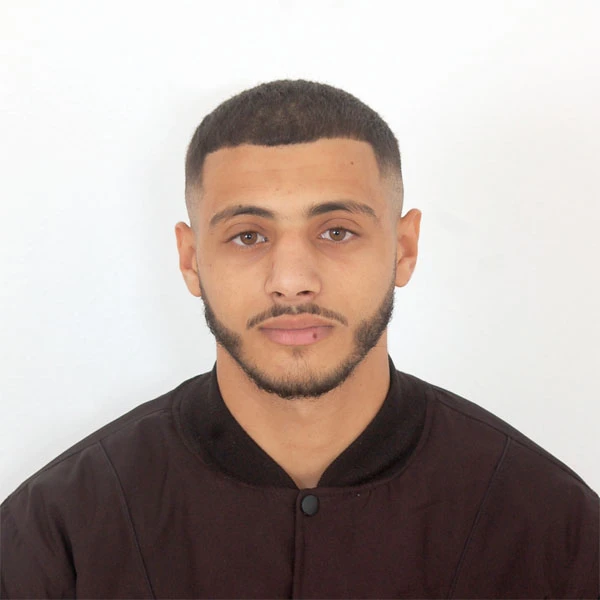
SERGIO
PENTESTER
DISCOVERED CVES
Vulnerabilities I discovered and reported
- View advisory
CVE-2026-XXXXX
Technical details and severity will be published when the advisory is available
- View advisory
CVE-2026-XXXXX
Technical details and severity will be published when the advisory is available
CERTIFICATIONS
Certifications that back up my work
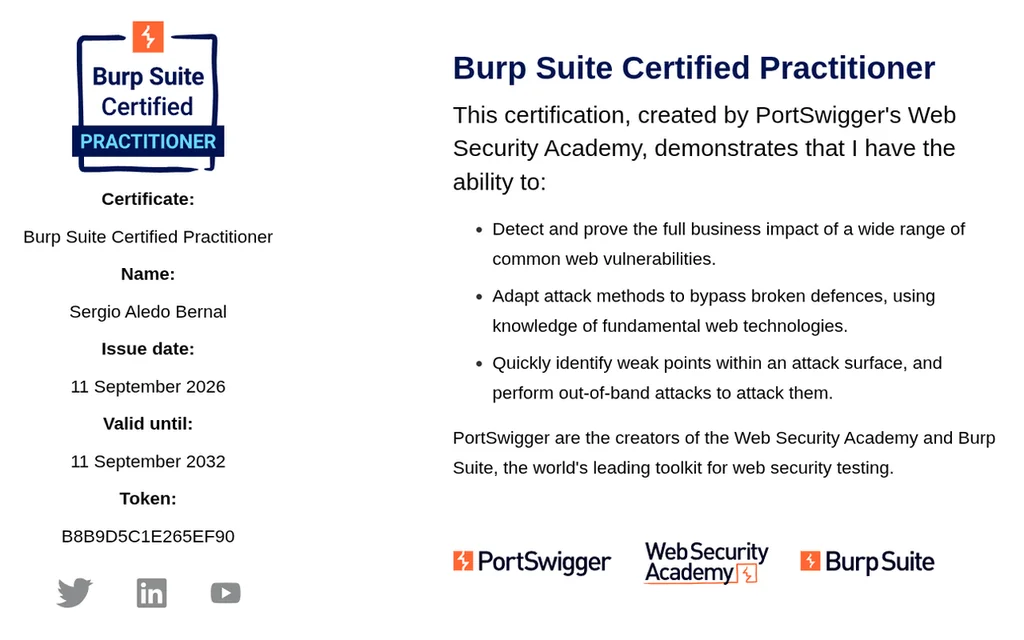
BSCP (Burp Suite Certified Practitioner)
PortSwigger